Microsoft Solutions Partner
Microsoft Intune Consulting Services
Deploy and govern Microsoft Intune with a clear plan for enrollment, compliance, Autopilot, app deployment, endpoint security, updates, and SCCM-to-Intune migration.
Experienced across Intune, Microsoft 365 security, identity, and managed endpoint operations.
Years
Endpoint Projects
Microsoft Specialists
Microsoft Solutions Partner
Built across the major agent ecosystems
Copilot Studio
Azure AI Foundry
AWS Bedrock
Google Vertex AI
OpenAI
LangChain / LangGraph
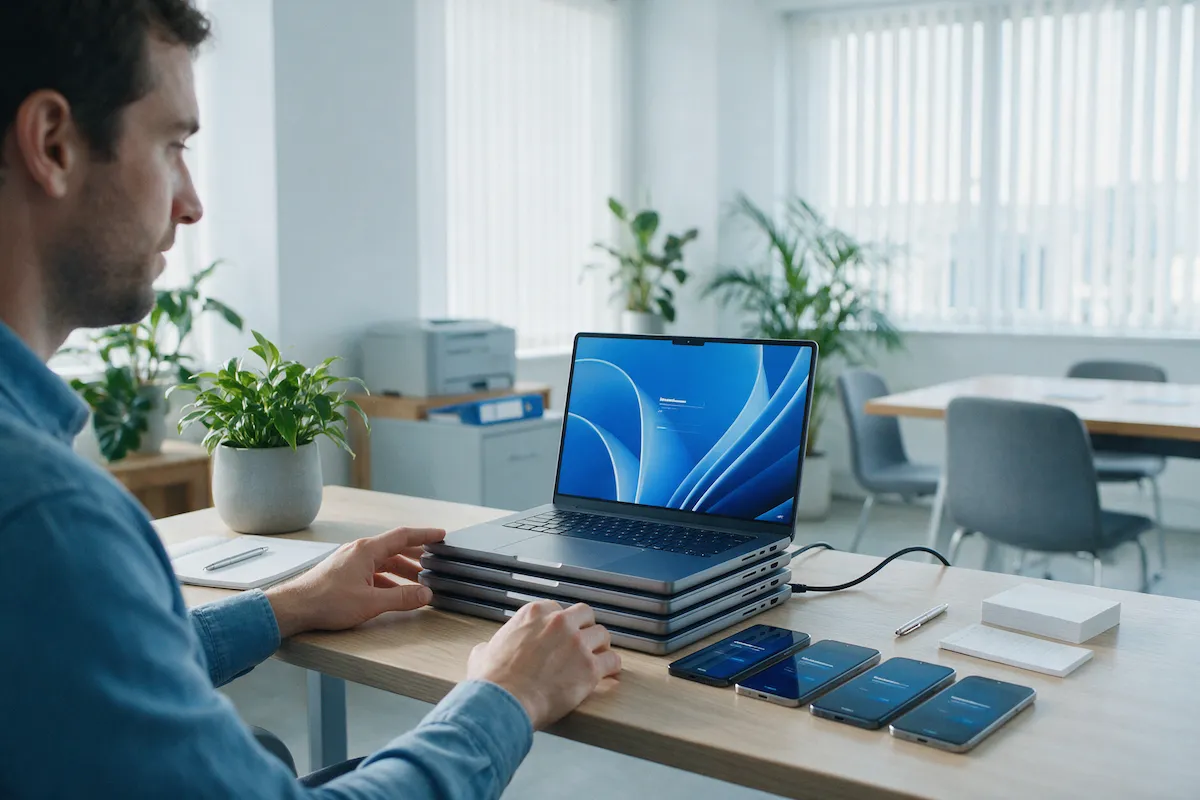
Take Control of Your Endpoint Environment
01
Unmanaged or inconsistently managed devices with limited visibility?
02
Still on SCCM/ConfigMgr and ready to move to cloud management?
03
BYOD devices accessing company data without MAM protection?
Zero Trust blocked by missing enrollment, compliance, or patch signals?
What We Do
Secure, Manage & Govern Every Device
01
Every Device Managed
Manage Windows, macOS, iOS, and Android devices across corporate, remote, shared, and BYOD environments from a centralized platform.
02
Security & Zero Trust Built In
Combine Intune compliance, encryption, Microsoft Defender, and Entra Conditional Access to make device trust part of your Zero Trust strategy.
03
SCCM to Cloud-Native Management
Move from SCCM/ConfigMgr to Intune through co-management, phased workload migration, and a practical path toward cloud-native endpoint management.
Zero-Touch Provisioning
Use Windows Autopilot to configure new devices with the right policies, applications, and security settings without traditional imaging or hands-on IT.
05
Apps, Updates & Compliance Governed
Deploy applications, manage update rings, enforce policies, monitor compliance, and remediate issues consistently across your device estate.
06
Visibility & Control at Scale
Gain centralized reporting and operational visibility across devices, applications, policies, compliance, and endpoint health for easier ongoing management.
Technical Capabilities & Production Readiness
01
Enrollment architecture for corporate devices, BYOD, shared devices, and remote users.
02
Security baselines, compliance policies, encryption, and role-based administration.
03
Policy conflict testing, report-only conditional access staging, remediation, and rollback planning.
Win32, LOB, Microsoft Store, and mobile app deployment with pilot validation.
05
Update rings, compliance reporting, monitoring views, and operational handover runbooks.
Our Services & Capabilities
01
Intune Assessment & Strategy
Assess devices, gaps, and rollout needs to define the right Intune strategy.
- Device inventory & gap analysis
- Intune strategy
- Rollout plan
02
Device Enrolment & Autopilot
Enroll Windows, macOS, iOS, Android, and BYOD devices; enable Windows Autopilot for zero-touch setup.
- Multi-platform enrolment
- Windows Autopilot
- BYOD enrolment
03
Configuration & Compliance Policies
Configure baselines, compliance rules, restrictions, and profiles for continuous enforcement.
- Security baselines
- Compliance policies
- Configuration profiles
04
Application Deployment & Management
Deploy, configure, and update Win32, LOB, Microsoft Store, and managed mobile apps centrally.
- Win32 & LOB app deployment
- App configuration
- Managed app updates
05
Endpoint Security & Defender Integration
Integrate Defender for Endpoint, enforce encryption, and use compliance for conditional access.
- Defender for Endpoint integration
- BitLocker / FileVault
- Compliance-gated access
06
SCCM / ConfigMgr Migration
Migrate SCCM/ConfigMgr through co-management, then shift workloads to cloud-native Intune.
- Co-management setup
- Workload migration
- SCCM retirement path
07
Update Management & Reporting
- Windows Update for Business
- Update rings
- Compliance reporting
Need broader M365 security beyond devices? See M365 Security Services. Need identity?
Find the Right Intune Engagement for Your Environment
| Your situation | What we deliver | Typical outcome |
|---|---|---|
“Devices are unmanaged or partially managed” | Intune deployment & enrolment | Every device enrolled, visible, and controlled |
“We’re still on SCCM/ConfigMgr” | SCCM-to-Intune migration | Cloud-native device management, SCCM retired |
“BYOD and personal phones aren’t secured” | MAM + BYOD policies | Company data protected on personal devices |
“We need zero-touch device provisioning” | Windows Autopilot deployment | New devices self-configure, ship-to-user |
“Updates are left to users” | Update management + rings | Patching governed, compliance visible |
“Devices aren’t feeding Zero Trust” | Compliance + conditional access integration | Device trust as a Zero Trust pillar |
“We need apps deployed centrally” | App deployment & management | Users have the right apps, IT controls them |
Not sure where to start? The free Intune assessment identifies the right engagement path and the first rollout wave.
Our Intune Delivery Approach
Free consultation & assessment
We review your current device landscape, SCCM estate (if applicable), and goals. No cost, no obligation.
Strategy & design
We design the Intune architecture — enrolment methods, compliance policies, security baselines, app deployment, and Autopilot — tailored to your environment.
Pilot deployment
We deploy Intune to a pilot group across device types, validate policies, and confirm the approach before scaling.
Enrolment & policy rollout
We enrol devices in waves, apply configuration and compliance policies, and deploy apps — with communication and support.
Security integration
We integrate Defender for Endpoint, enforce encryption, and connect device compliance to conditional access for Zero Trust.
SCCM migration (if applicable)
We set up co-management, migrate SCCM workloads to Intune incrementally, and plan the path to cloud-only.
Monitoring, updates & ongoing management
We set up update rings, compliance reporting, and monitoring — and can provide ongoing managed-endpoint support.
It starts with a free Intune assessment. No obligation.
Why Star Knowledge
| Criteria | Star Knowledge | In-House IT | Generic MSP |
|---|---|---|---|
Intune depth | Specialist, certified | Learning curve | May focus on basic enrollment |
Security integration | Defender, encryption, conditional access | MDM-only | Basic |
SCCM migration | Co-management → cloud-native path | Risky / untested | May require separate migration expertise |
Autopilot | Designed and deployed | Not configured | Limited |
BYOD / MAM | Properly secured | Uncontrolled or blocked entirely | Inconsistent |
Update management | Governed with rings and reporting | Ad-hoc | Set-and-forget |
Zero Trust alignment | Device trust as a pillar | Not connected |
May require separate security architecture support |
Track record | 40+ endpoint projects | In-house only | Mixed |
Case Studies
Manufacturing company, 500+ devices across 4 sites.
SCCM → Intune co-management → cloud-native, Autopilot
On-premises SCCM was ageing and couldn’t manage the growing remote and hybrid workforce.
Migrated via co-management, moved workloads to Intune incrementally, and deployed Autopilot for new devices.
Professional services firm, 250+ users, heavy BYOD.
Intune MDM/MAM, Defender for Endpoint, conditional access
Personal phones and tablets accessed company data with no protection — a compliance and security risk.
Deployed Intune MAM for BYOD, enrolled corporate devices, integrated Defender, and connected compliance to conditional access.
Financial services firm, 300+ Windows devices.
Windows Autopilot, Intune compliance, conditional access
Manual device imaging was slow, and devices weren’t feeding trust signals into conditional access.
Deployed Autopilot for zero-touch provisioning and connected device compliance to conditional access for Zero Trust.
Industries We Serve
Financial Services
Compliant, encrypted, managed devices
Healthcare
HIPAA-aligned endpoint security and clinician devices
Manufacturing
Multi-site device management and frontline tablets
Professional Services
BYOD-friendly with corporate data protection
Legal
Confidential-data protection on every device
Retail
Store devices, kiosks, and shared-device management
Education
Student, staff, and shared-device management at scale
Technology & SaaS
Developer devices with security and flexibility
From a first Intune pilot to enterprise-wide endpoint management with SCCM retirement, we scale to fit.
Insights
Endpoint Management, Zero Trust & Copilot Readiness (2026)
In 2026, managing devices isn’t just about keeping laptops updated — it’s a core security pillar. Zero Trust requires device trust: conditional access asks “is this device enrolled, compliant, and healthy?” before granting access. An unmanaged device is an untrusted device, and untrusted devices are where breaches start. With Copilot accessing data across your M365 estate, the device it runs on matters more than ever.
01
Device compliance feeds conditional access — managed, healthy devices are what Zero Trust device trust means
02
03
Why does device management matter for Zero Trust and Copilot?
Because Zero Trust asks “is this device trustworthy?” before granting access — and Copilot accesses your data from the device it runs on. An unmanaged, non-compliant device can’t answer that question and shouldn’t be trusted with your data or your AI. Intune makes devices a verified, managed pillar of your security model.
Frequently Asked Questions
What is Microsoft Intune consulting, and what do you cover?
Intune consulting deploys, secures, and governs Microsoft’s cloud endpoint management platform. Star Knowledge covers assessment, enrollment, compliance, Autopilot, app deployment, Defender integration, SCCM migration, updates, and BYOD/MAM.
Can you migrate us from SCCM/ConfigMgr to Intune?
Yes. We use co-management to move SCCM/ConfigMgr workloads to Intune in stages, then plan a cloud-native path when ready.
Can Intune manage both corporate devices and BYOD?
Yes. Corporate devices use MDM for full control; BYOD uses MAM to protect company apps and data without wiping personal content.
What is Windows Autopilot, and should we use it?
Windows Autopilot lets devices self-configure after sign-in with assigned policies, apps, and security — no manual imaging or IT hand-holding.
How does Intune connect to Zero Trust and conditional access?
Intune reports whether a device is enrolled, compliant, encrypted, and healthy. Conditional access uses that signal to grant, limit, or block access.
How much does Intune consulting cost, and how long?
Intune consulting is typically estimated at $400–$600 per consulting day. Total cost depends on device count, platforms, SCCM/ConfigMgr scope, app packaging, Autopilot, security requirements, and rollout complexity.
Do you manage updates through Intune?
Yes. We configure Windows Update for Business, update rings, compliance reporting, and remediation through Intune.
Can you provide ongoing managed-endpoint support?
Yes. We can monitor compliance, manage updates, deploy apps, tune policies, and support broader M365 Managed Services.
Book My Free Intune Assessment
Tell us the task you have in mind. We’ll assess whether an agent suits it, at what autonomy level, and what the first step should be.
- No cost, no obligation
- Typically responds within 4 business hours
- Confidential — your data isn't shared
- Microsoft Solutions Partner for Modern Work
Typically responds within 8 business hours · Confidential